Cybersecurity video production
Cybersecurity video production that speaks SOC.
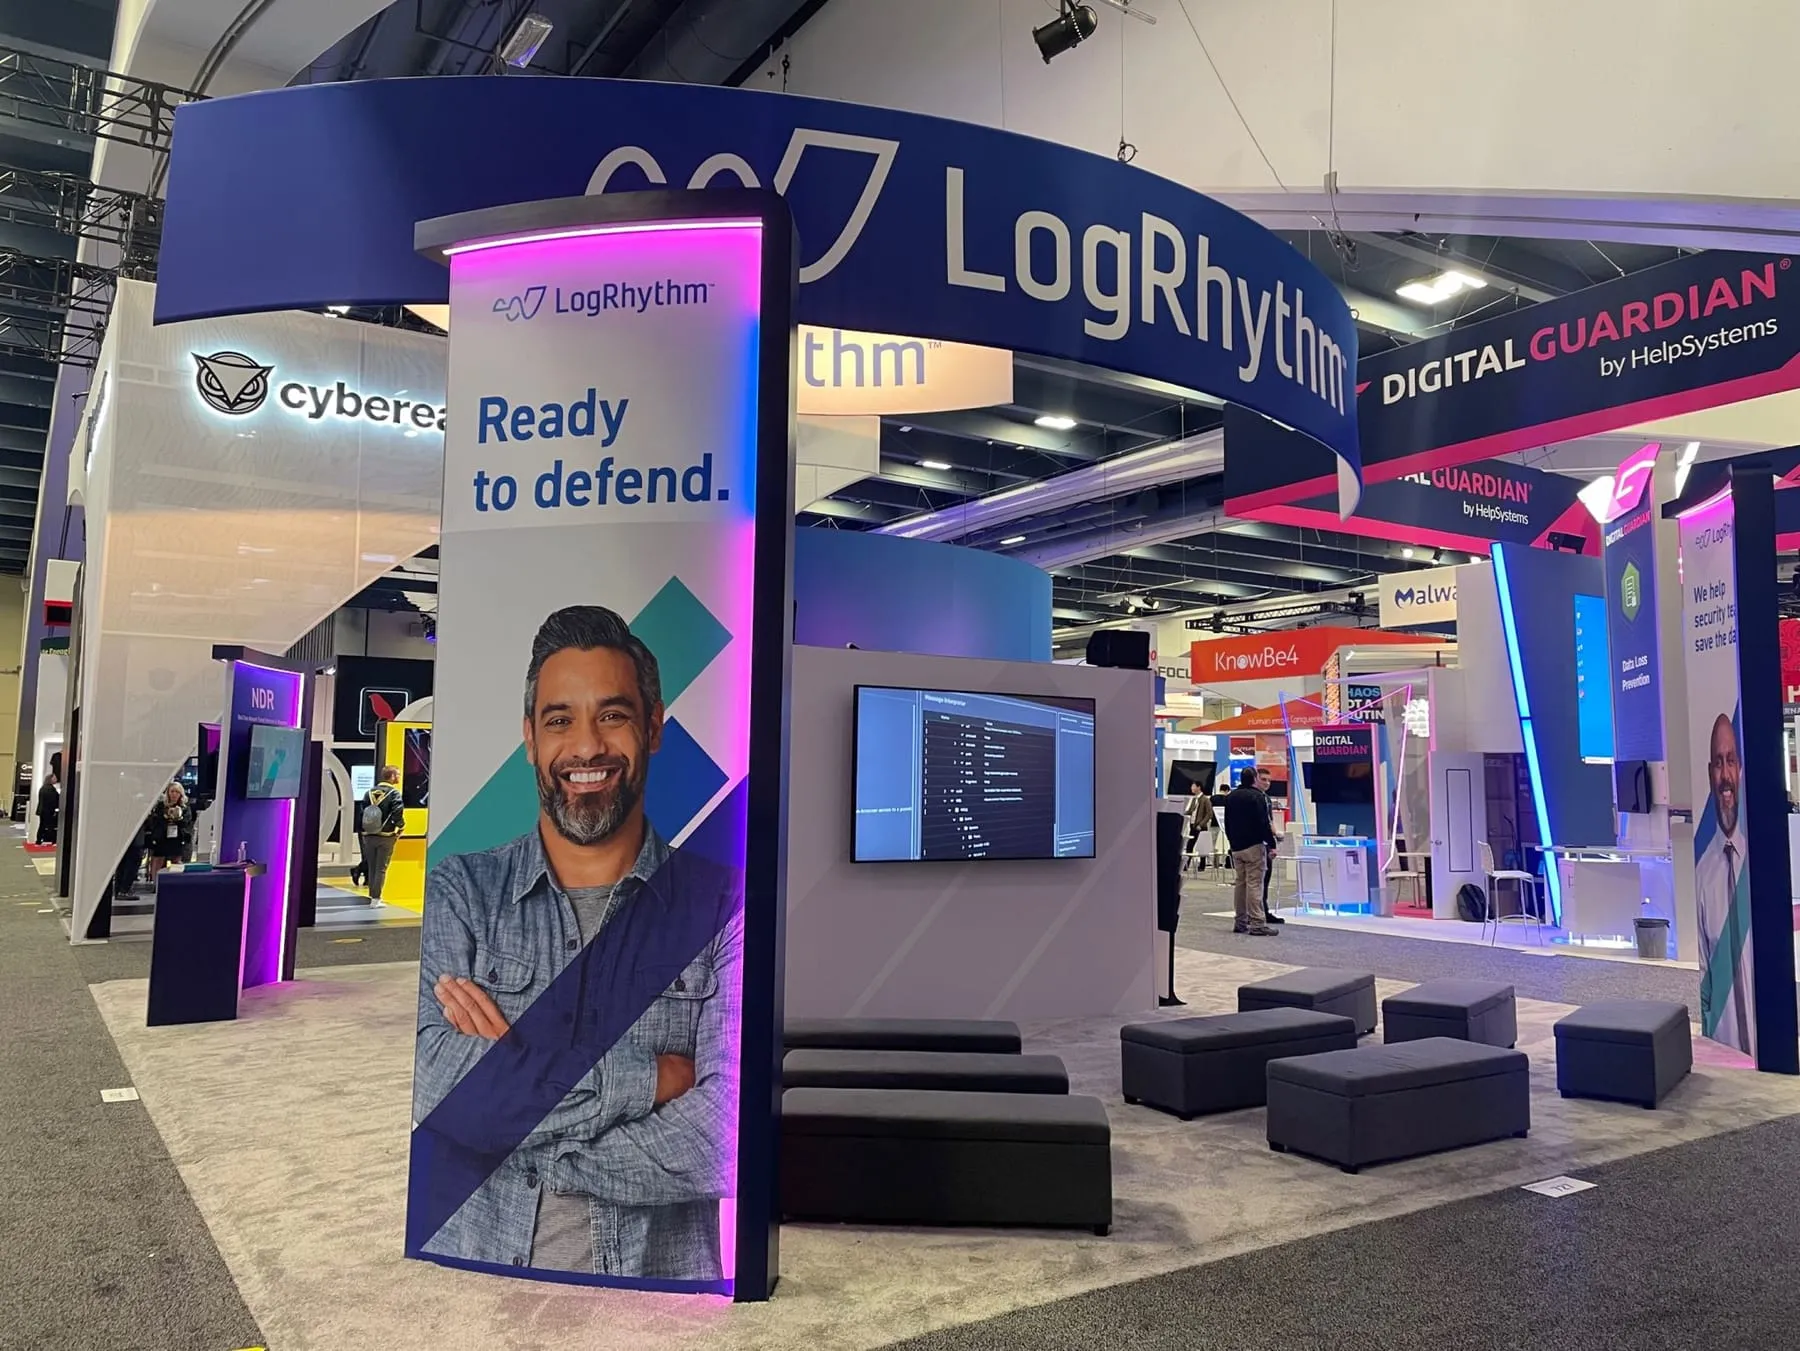
Booth loops, product explainers, and use case films for security companies, made by a team that has shipped RSAC booth content every year since 2017. Your buyers can smell fluff from across the hall. We don't make any.
Security clients
Why security video is its own craft.
Every vendor on the RSAC floor says platform, AI, and zero trust. The attendee walking past decides in two seconds whether your booth is different, and they decide with the sound off. A security loop has to sell silently, from thirty feet, against an LED wall arms race.
Then there is the buyer. A CISO or a SOC lead will switch off the moment a video oversimplifies the threat or waves its hands at how the product works. We write for that person: accurate, specific, and still clear enough for the board.
We have done this across the security stack: SIEM, SOAR, UEBA, endpoint, cloud, and human risk. The vocabulary is already ours. The story is yours.
Proof
Made for security companies.
Booth loops that ran at RSAC, explainers that sales teams still send, conference openers, and a kickoff film. Click any of them.


Transcripts
Read what the videos above say. Speaker names are from the films; the text is lightly cleaned from the spoken word.
Swimlane: phishing response
We all start small. An idea becomes a business, and that business grows into an enterprise. Strong, profitable, built to last. But with great power comes great vulnerability. The average organization faces over 10,000 new security alarms every day, and the complexity and volume frequently overwhelms the analysts tasked with stopping them. Current IR processes make analysts manually navigate multiple specialized platforms to identify, respond to, and document every threat. These processes are inefficient and difficult to learn, and lead to unresolved or unseen alerts. The potential for human error is high. But the problem is not your staff, it's your system.
Swimlane delivers a better, more accurate solution through security automation and orchestration that adapts to fit the people, processes, and technologies you already have in place. It easily integrates with other systems and adapts over time to keep up with the pace of IT innovation. An easily customized, intuitive interface allows you to simplify administrative tasks without sacrificing flexibility.
Your team's ability to rapidly respond to an incident is critical, and no viable threat is too small to investigate. Phishing is one of the most common methods of infiltration because it's both effective and simple to execute, and most security operations are dependent on a growing combination of tools and manual processes to detect, research, and respond to the daily flood of potential attacks. This exhausts personnel, wastes precious time, and leads to costly mistakes.
Swimlane drastically reduces resolution times while minimizing the potential for error by automating significant portions of the incident response process. This includes steps like submitting data to threat intelligence platforms for analysis, submitting attachments to a sandboxing platform for additional inspection, and quarantining infected devices and notifying impacted users. By typically automating as much as 80 to 90% of an IR workflow, Swimlane drastically increases the response capacity of your SOC without adding overhead.
At its core, cybersecurity is driven by high-value expert analysis. Burdening your security team with manual tasks like copying and pasting evidence, sending email notifications, and opening trouble tickets leads to slow response times, inconsistent investigations, and unresolved alerts. Through automation and orchestration, Swimlane equips your SOC for maximum efficiency and ROI. Protecting your business may not be simple, but it can be a lot easier.
How Securonix is different
Securonix isn't like your traditional SIEM solution. Yes, we identify cybersecurity threats across your cloud, on-premise, and edge devices. But say goodbye to the hassle of managing your SIEM infrastructure. Our SIEM-as-a-service brings your data into one robust cloud platform that is managed 24/7 by Securonix, delivering a quick return on investment with our rapid deployment process. Analytics is seamlessly delivered and updated on an ongoing basis, so you can focus on threats against your organization. As a Gartner Magic Quadrant leader, Securonix delivers an analytics-powered SIEM to enable unparalleled threat detection and response with minimal operational overhead.
How does Securonix enrich your data for threat detection? Our architecture collects huge amounts of security data across a variety of data sources and enriches them in real time with critical user and business context. Analysts gain the ability to search on enriched events across live and historic data for unmatched threat hunting and investigation. Securonix's cloud-native approach ensures elastic scalability to optimize cost and performance, while enabling fast and effective detection and response.
Now, we know that data collection is only half the story. What makes Securonix advanced analytics different? To catch the modern attacker, you need to closely monitor the behavior of users, computers, and IoT devices across an organization's network for suspicious anomalies. Securonix utilizes patented machine learning to monitor behavior patterns compared to baseline normal and detect suspicious deviations or anomalies. Securonix uniquely stitches together anomalies using threat chains that reduce noise for the analyst and give them a clear view of threat escalation. To enable users to act on and remediate threats, Securonix includes built-in case management and SOAR capabilities for investigation and response, providing an end-to-end security operations platform that minimizes your mean time to respond.
How does Securonix empower you to be immediately effective? With Securonix, you'll hit the ground running. On day one, your Securonix solution will run hundreds of pre-built use cases, covering popular data sources from firewalls to endpoint tools to cloud services. These use cases are mapped to the MITRE ATT&CK framework, covering common tactics and techniques. With the Securonix sandbox, you can test and tune the use cases for effectiveness using our self-learning algorithms and deploy to production without disruption. Outmaneuver advanced threats with the Securonix Next-Gen SIEM. Visit securonix.com today to request a demo.
Spyderbat: Attack Tracing and Intercept
A chasm exists between threat detection and response. It's defined by the manual effort required to triage and investigate security alerts. Its depth is measured by alert volume. Its width is measured by the time required to thoroughly investigate them. There are too many alerts. We rely on priority to sort what gets our attention. Existing tools only detect individual symptoms, requiring manual expertise to determine the full picture and root cause. In our investigations, we struggle to retrace the attack under enormous time pressure and constraints. This combination of alert volume and manual effort creates a constant state of anxiety. What did I miss?
What if we could bridge the chasm with a new approach? One that instantly illuminates false positives, catches would-be false negatives, and accurately spots emerging attacks. An approach that radically reduces alert volume and compresses investigation time. This is Spyderbat Attack Tracing and Intercept. A key to ATI is the operations plane. The operations plane proactively links causal connections between ground-truth activities. Causal connections exist within and across systems over potentially long periods of time. Using your existing threat detection systems such as SIEM, EDR, firewalls, or cloud-based protection, security information is layered on the operations plane, illuminating false positives and credible attacks. Enriched context such as threat intelligence, cloud tags, and suspicious activities adds color to the attacker's path.
Fused together, the operations plane links seemingly disparate security events and benign activity into a live trace of the attack. Attack traces present a clear, accurate, and complete depiction of all causally connected steps leading to and following a security alert. This instant, clear view enables immediate intercept and complete eradication of the attack. Spyderbat's game-changing Attack Tracing and Intercept is fast, accurate, complete. Intercept the attack with Spyderbat ATI. No longer worry about what is missing. To see Spyderbat ATI in action, go to spyderbat.com.
LogRhythm and Palo Alto Networks: ransomware response
Cybercriminals are compromising organizations at an unprecedented rate. To counter these attacks, security teams must leverage multiple security solutions to build and strengthen security operations. By enabling comprehensive end-to-end Threat Lifecycle Management, LogRhythm and Palo Alto Networks work together to provide a streamlined solution to keep your company one step ahead.
Picture this: a financial analyst for your organization receives an email containing an infected PDF disguised as an accounts payable dispute. Upon opening the file, they're greeted with an ordinary error. Assuming the PDF is simply corrupted, they notify the sender and continue their day. Meanwhile, back at the SOC, the LogRhythm security intelligence platform detects indicators of infection as malware embedded in the PDF sets to work. Within minutes, a high-priority corroborated alarm is triggered with a risk rating of 95, indicating a ransomware variant has been identified in the network. You need to respond effectively and immediately. Don't worry, LogRhythm SmartResponse has automatically fired, instantly locking down and quarantining the endpoint in question.
Once the incident is fully triaged, lateral movement halted, and encryption has ceased, it's time to create a new case and investigate. With just a click, the full details of the attack are displayed. Immediately you see the high-priority alarm was triggered by four low-priority alarms. These reveal a number of incidents have occurred, including command-and-control beaconing, unauthorized process activity, and excessive file access. Individually, these data points don't necessarily signify a problem, but seen together, LogRhythm was able to rapidly detect a live ransomware threat.
Moving to the alarm dashboard, the threat list communication alarm exposes yet another SmartResponse action. This one is configured to require manual approval. One click automatically adds the malicious command-and-control IP address to a block list in your Palo Alto firewall, preventing other users from being affected by the same attack. After pivoting into Palo Alto to confirm the IP address has been blocked, you jump back to LogRhythm, add notes for the postmortem, and close out the investigation.
This case was just an unsuspecting employee falling victim to a ransomware attack. This breach could have led to widespread encryption of corporate data, resulting in significant expense, lost productivity, and a damaged reputation. Fortunately, LogRhythm and Palo Alto Networks provided effective end-to-end Threat Lifecycle Management, enabling you to rapidly detect, respond to, and remediate a potentially damaging cyber threat and prevent future harm, all from one screen. Join us at logrhythm.com.
KB4-CON opener: human risk management
In every era, humanity has faced challenges and risen to overcome them. We innovate, we adapt, we thrive. But today, technology evolves at lightning speed, bringing both incredible opportunities and unprecedented risks. Now we stand on the edge of a new era where the stakes have never been higher. At KnowBe4, we are not replacing human intelligence. We're supercharging it by using AI to outsmart AI. We're creating a future where machine learning and human intuition work in perfect harmony.
Our adaptive defense reimagines what's possible. It's not just about responding to threats. It's about anticipating them, learning from them, and evolving faster than they can. Your role has never been more important. You are the ones seeing around the corner to transform human risk into human resilience. Together, we are creating a safer, smarter world, a world where human expertise and artificial intelligence unite to achieve the extraordinary. Because when we work together, there's no limit to what we can accomplish. Welcome to the cutting edge of human risk management. Welcome to KB4-CON.
Securonix Threat Labs: why security content matters
Our customers' mission is to protect themselves, and a platform for normalized data and queries is part of that journey of protecting oneself, but the content we put on top of the SIEM enables better protection. I see SIEM as the platform and content as the operating system, or SIEM as the mobile phone and content as the applications that the end users use today. So having the right content is imperative for multiple reasons, but the primary reason here is that we don't want organizations to spend their time trying to hunt, trying to build net new content. They should be more focused on securing their environment, so having the right content emphasizes that.
Let's talk about the critical issues that exist in SIEM today. Configuration is tedious, SIEM is just too noisy, or it needs expert analysis. Fundamental to solving any of these problems is having the right content, which is precise, which is actionable, it's for their geo, for their organization, which is custom delivered for them, and that's exactly what Securonix does.
So we take a three-pronged approach. We start with threat research. Our threat research team keeps an eye on all active and emerging threats. They run those in our labs, look at the behaviors of how the attack manifests, and they work on translating that behavior into detection content.
We also take a more threat-hunting-based approach as well, where we sift through tons of logs and use those insights to augment what we already have as content. The third part is our intelligence and community channels, where we also partner with other technology vendors and other communities that we are a part of, from a research and detection standpoint, and use the insights that we learn from there to improve our content.
We produce content in multiple forms. We start with threat advisories and blogs. That's the first thing that we intend to publish as we keep an eye on any active and emerging threat. Additionally, we have a new bot that we launched in the last year called Autonomous Threat Sweeper, and what that bot does is consume the intelligence, consume the TTPs that we see from our lab observations, and run a historical scan to see if there's any presence of these threats at customer environments.
So we publish the inputs that the bot consumed in the form of intelligence that goes out, and we've made it open source as well for other customers and the community to consume. The third form is actually our detection content, which goes into our library, which is made available as part of a cloud-based service to our customers.
ATS, or Autonomous Threat Sweeper, is nice because you can find it once in somebody's environment, or create it because of threat research, open threat research. You can say here are some patterns that we should be looking for, here are some of the vulnerabilities that people have been looking at or exploiting, look for identifiers, indicators of those. And then if you find it in somebody's environment, or if you create it on the fly, you can then apply that across all of the clients so that everybody gets the benefit.
What we make for security teams
Four jobs, one vendor.
Trade show loops
Silent-first booth loops built for RSAC and the security show circuit. Thirty feet, no audio, two seconds to earn a stop.
Product explainers
SIEM, SOAR, UEBA, human risk, cloud security. Explained to a CISO without dumbing it down and without drowning it in acronyms.
Use case and integration films
A real attack scenario, your platform stopping it, your partner integrations doing their part. Sales uses these for years.
Conference and kickoff videos
Openers and hype pieces for user conferences and sales kickoffs. The room goes quiet, then it goes loud.
Questions
Before you ask.
How much does a cybersecurity explainer or booth video cost?
A 30-second silent booth loop starts around $6,500 and a 90-second product explainer around $19,000, both at $215 per finished second with script, storyboard, design, animation, and revisions included. Live-action use case films and conference films are quoted per shoot day. Fixed quote after one call.
Which security companies have you worked with?
LogRhythm (RSAC booth content every year since 2017), KnowBe4 (KB4-CON and the Human Risk Management platform film), Securonix, Swimlane, and Spyderbat, across SIEM, SOAR, XDR, and human risk management.
Do you actually understand security products?
We have made videos for SIEM, SOAR, UEBA, endpoint, cloud security, and human risk platforms, including RSAC booth content for LogRhythm every year since 2017. You will not have to explain what a SOC is. You will have to tell us what makes yours different, and we will make that the story.
Can you work with unreleased product under NDA?
Yes. Most security launches we work on are under embargo until the show. We sign your NDA, work from staged environments or screen captures you provide, and keep review links private.
How fast can you turn a booth loop for RSAC?
Standard is nine to twelve weeks with delivery two weeks before doors open. Need a rush order? No problem. Call us with the date.
Can you capture a live product demo?
Yes. We record real UI at high resolution, then cut and annotate it so the demo reads on a wall or a phone. Clean captures, no shaky screen recordings.
What specs does an RSAC or Black Hat booth loop need?
Ask your exhibit house for the screen's native resolution and whether it needs a seamless loop; most booth screens are 1920 by 1080, and LED walls are custom canvases we build to the pixel. We deliver silent, seamlessly looping cuts of 30 to 90 seconds as ProRes and H.264, plus a stills set for the show guide, and we test the loop on the actual playback hardware whenever the exhibit house can provide it.
Your next launch deserves better than stock footage of a hoodie.
Tell us the product, the show, and the date. We'll come back with a plan and a quote within two business days.